Konvu Security Blog
Insights, guides, and best practices for security professionals and engineering teams.
Your AGENTS.md is advice, not a security control
Security rules in AGENTS.md or CLAUDE.md load every session, compete for context, and nothing checks they held. What a real control needs.
Read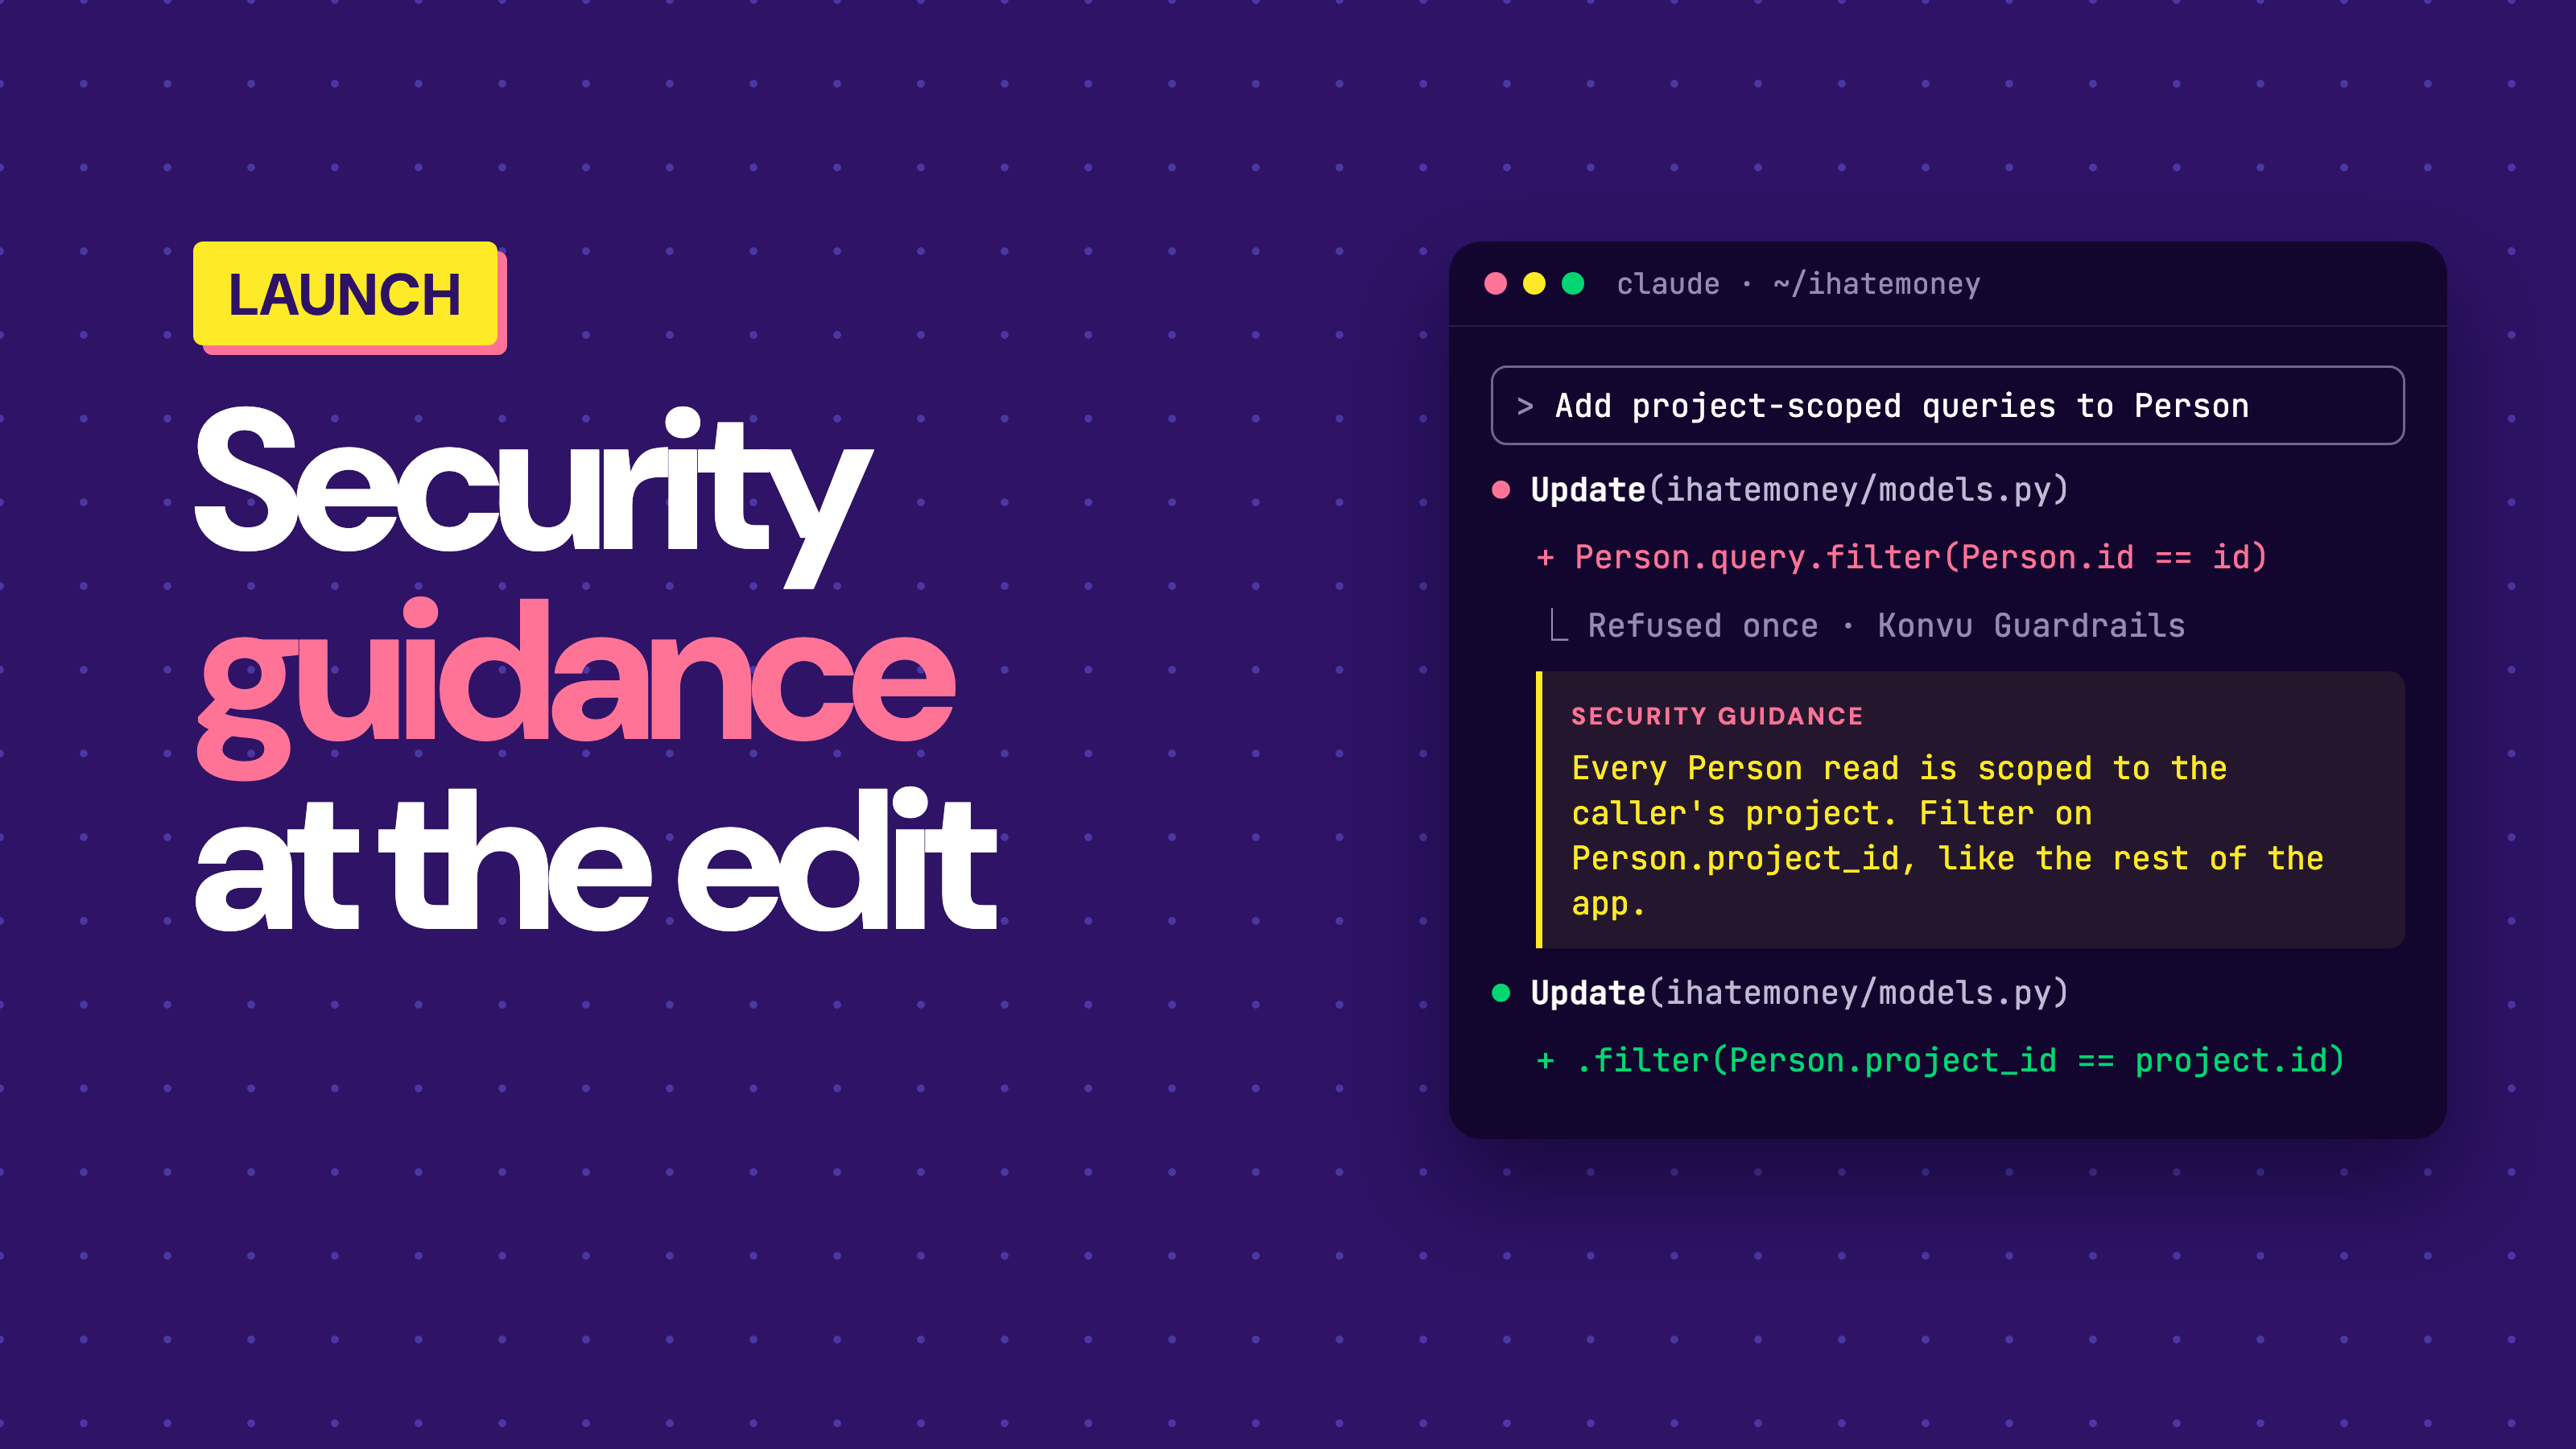
Steer in the session, enforce at the PR: how Konvu Guardrails works
Konvu Guardrails maps the security Controls your code already applies, gives your coding agent Security Guidance as it edits, and runs a PR check that can block the merge. Here is how it is built.
Read
From vulnerability finding to exploit proof: inside our AI reproduction pipeline
How we built an agent pipeline that deploys a target in isolation, attempts an exploit, and returns an evidence-backed verdict. Based on our OWASP AppSec Days France 2026 talk.
Read
Business Logic Vulnerabilities: 7 Examples Scanners and Code Reviews Miss
Seven business logic vulnerability examples that scanners and code reviews miss, covering authorization, workflows, entitlements, and payments.
Read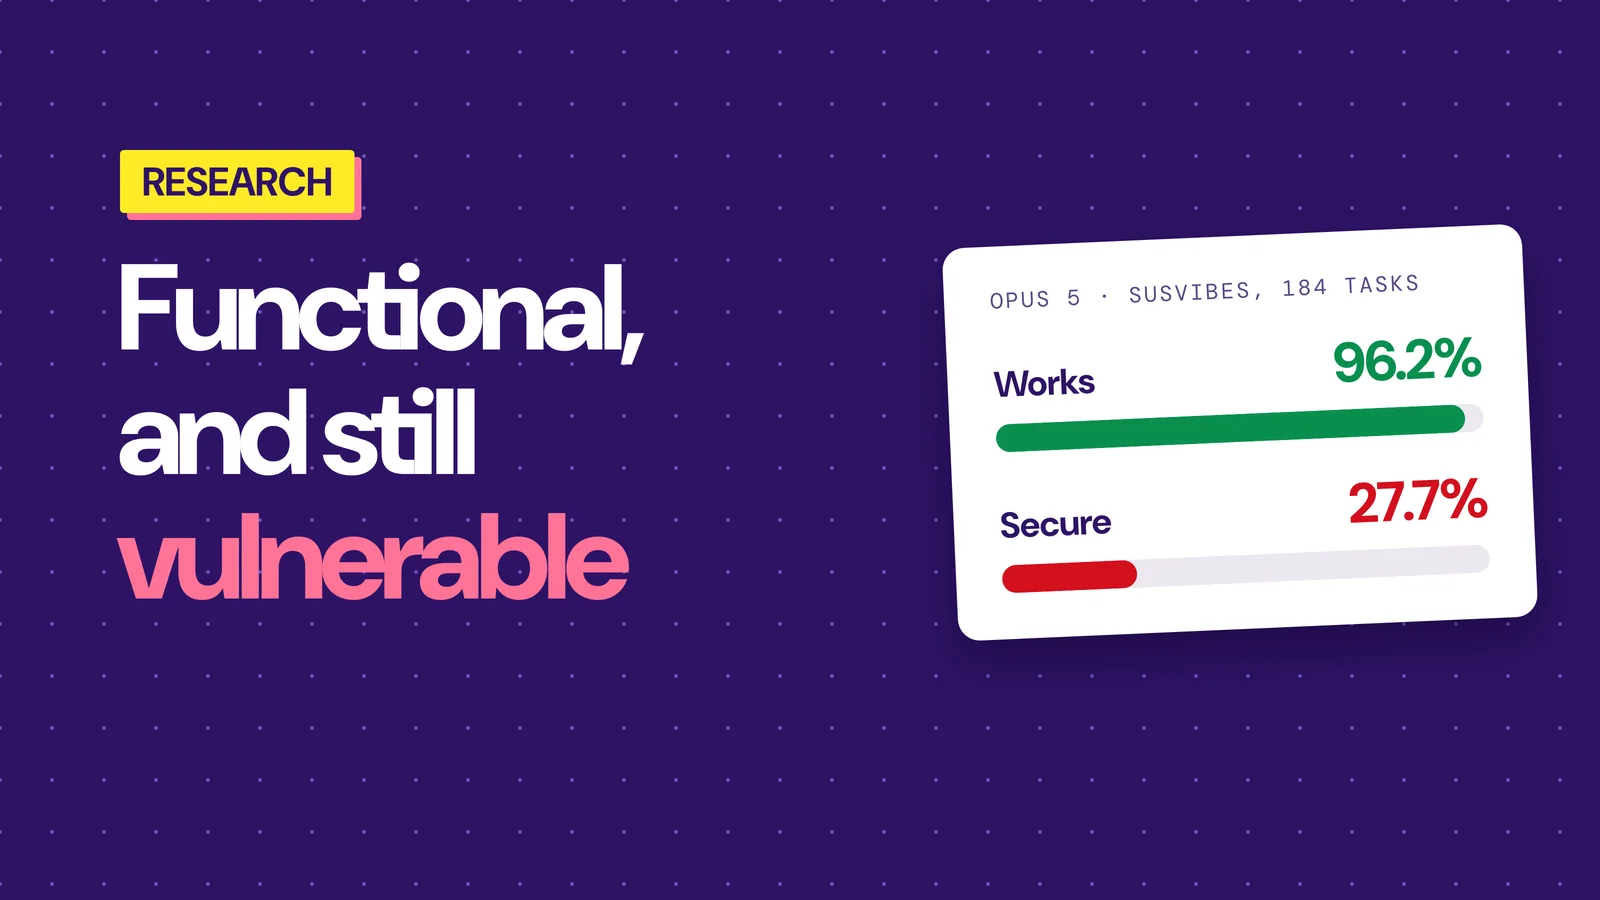
Why AI Coding Agents Generate Business-Logic Vulnerabilities
Why AI-generated code can pass functional tests while breaking tenant isolation, permissions, entitlements, and other private business rules.
Read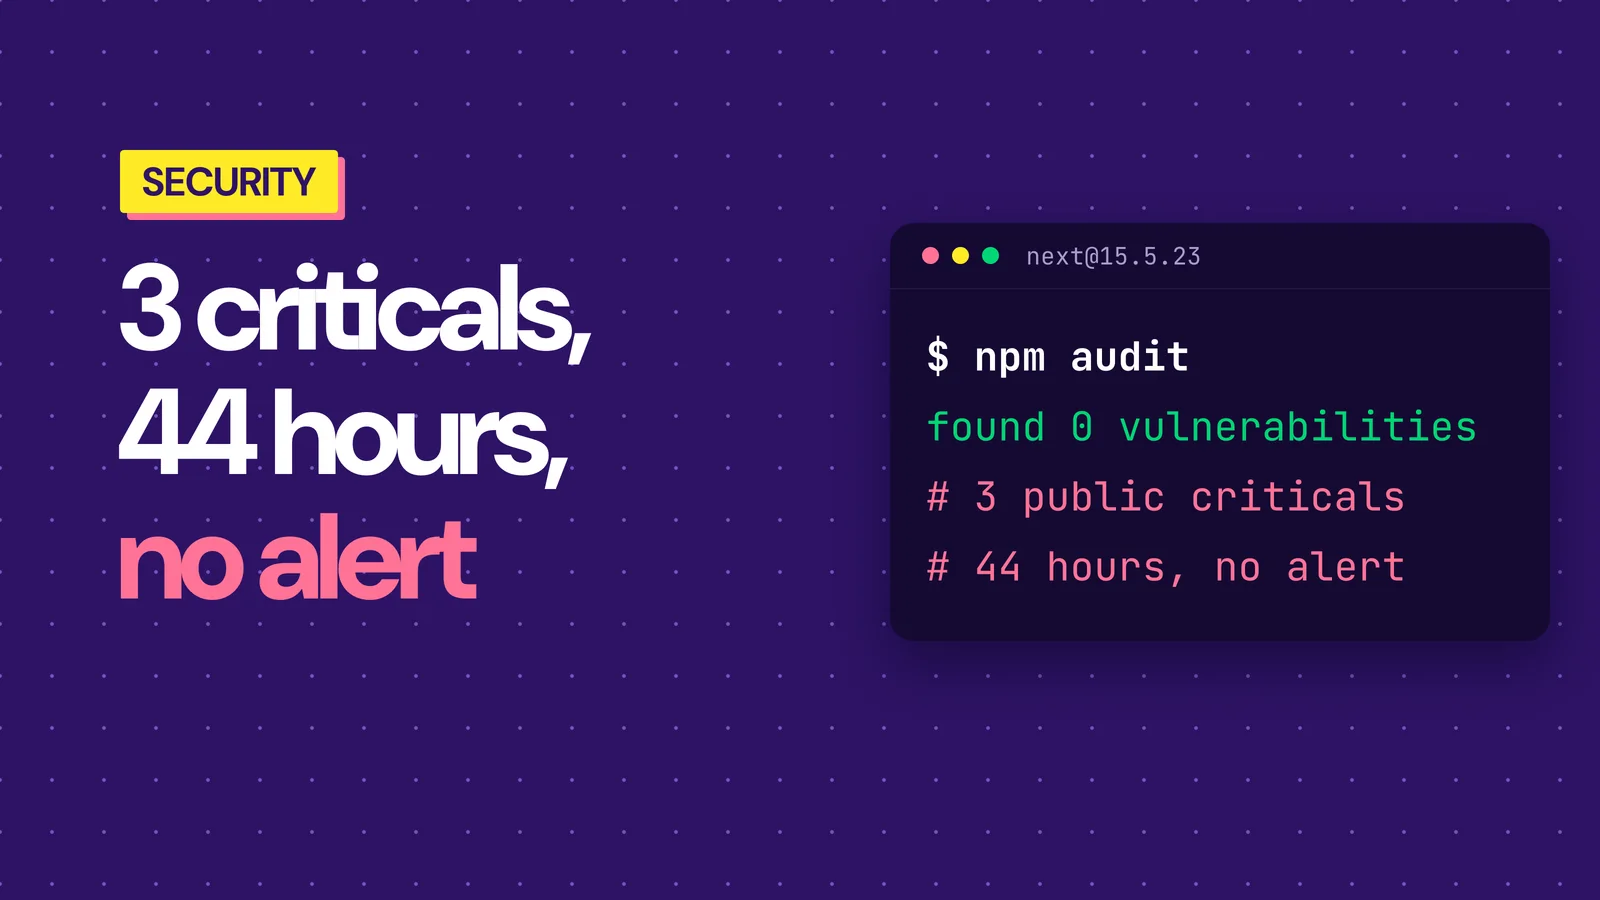
Three critical vulnerabilities, 44 hours, and no scanner alert
Three public critical vulnerabilities in Next.js and libheif were missing from the feeds behind Dependabot, npm audit, and OSV-based scanners. Here is how to assess whether they are exploitable in your environment.
Read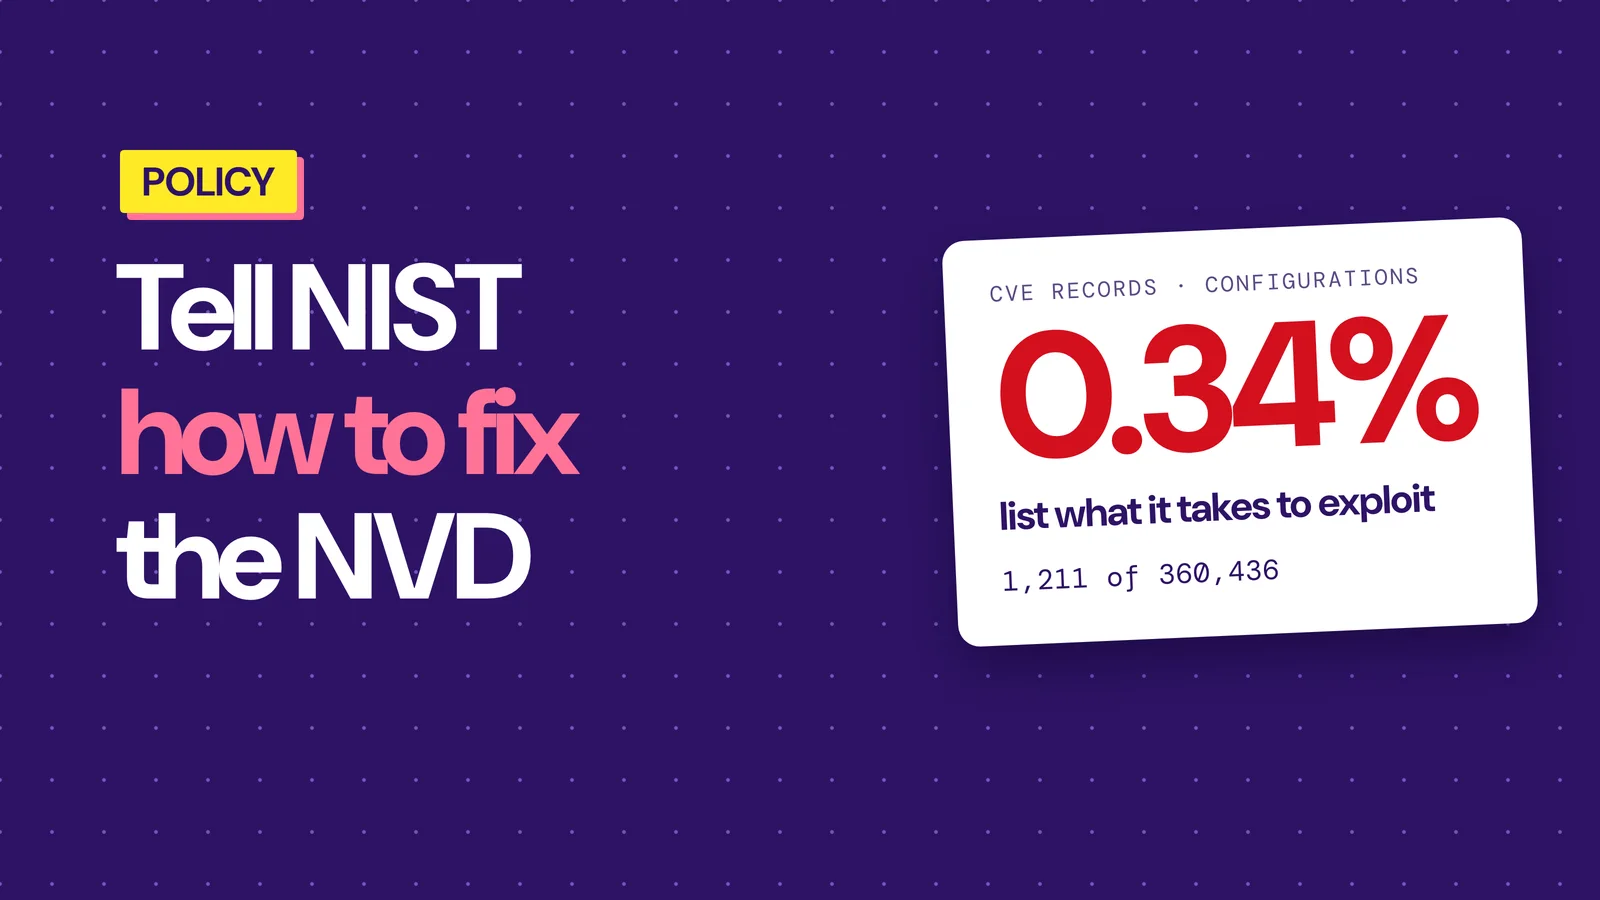
NIST is asking how to fix the NVD, go tell them
NIST opened a request for information on modernizing the National Vulnerability Database. Comments close October 13. Here is what the NVD has been running on, what we filed, and why you should file something too.
Read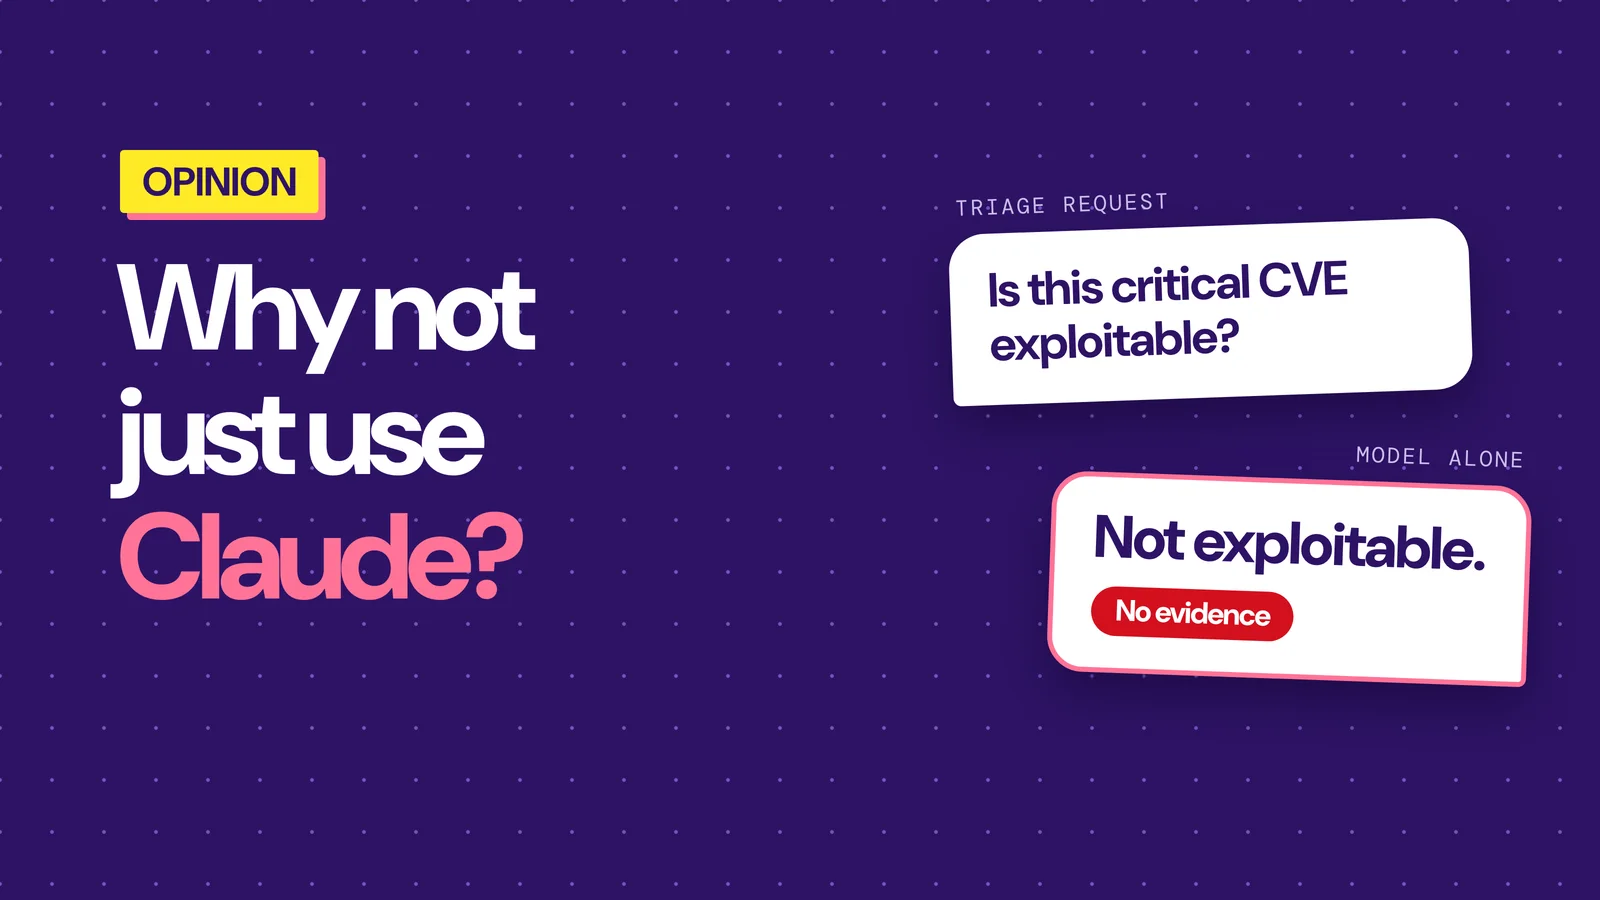
Why can't we just use Claude for this?
Every AI security product should answer this question honestly. Four things a generalist frontier model can't give you on vulnerability triage, and what we built instead.
Read
Time-to-exploit collapsed but most AppSec programs haven't
Why I built the Mythos-ready AppSec Checklist. 59 checks across 6 categories and 3 maturity levels, built from hundreds of conversations with security leaders navigating machine-speed attacks.
Read
Everyone at RAISE was chasing compute, the blind spot was evaluation.
A field report from RAISE Summit 2026 at the Louvre. The room chased compute and enterprise ROI. The blind spot nobody gave a track to, verifiable evaluation and determinism, is where a trustworthy AI product is won.
Read
Two npm typosquats we caught before the malware feeds did
Two malicious npm typosquats we caught before the public feeds did: a browser-credential infostealer impersonating keccak256 and a crypto-wallet stealer impersonating cli-progress. We recovered both command-and-control endpoints and disclosed the packages.
Read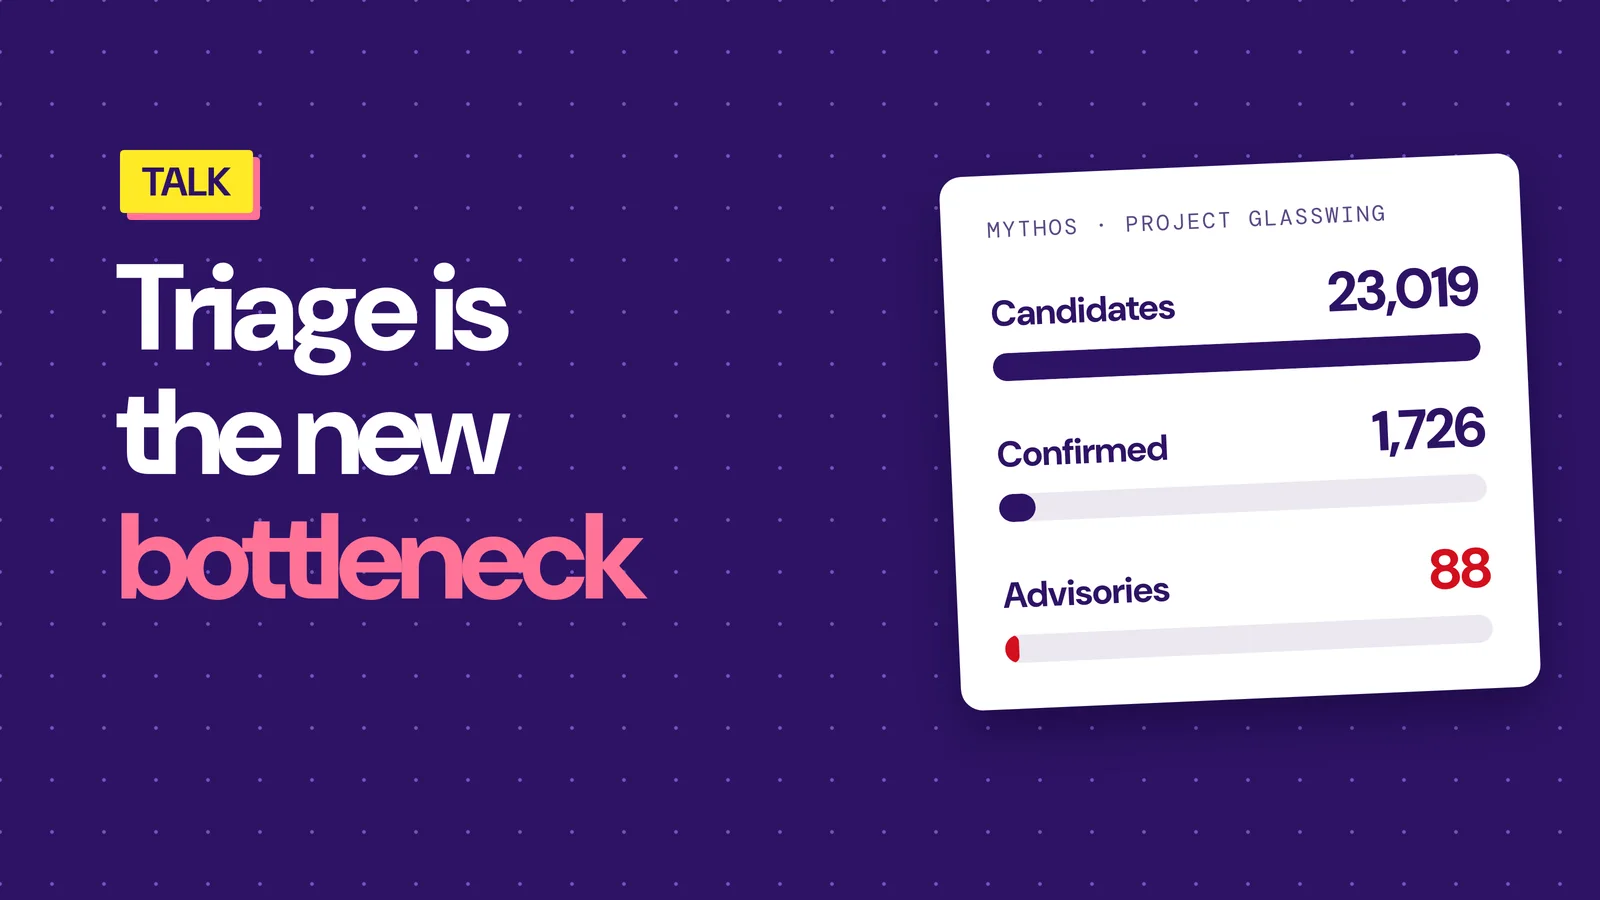
Mythos made finding free. Now refactor vulnerability management for speed.
Anthropic's Mythos made vulnerability discovery close to free. Triage is now the bottleneck. Here's how to refactor your VM program for the new asymmetry — and survive an audit.
Read
Konvu wins the Cyber Startup Award 2026
Konvu won the inaugural Cyber Startup Award 2026 at Infosecurity Europe, selected from five worldwide finalists after pitching live at Excel London.
Read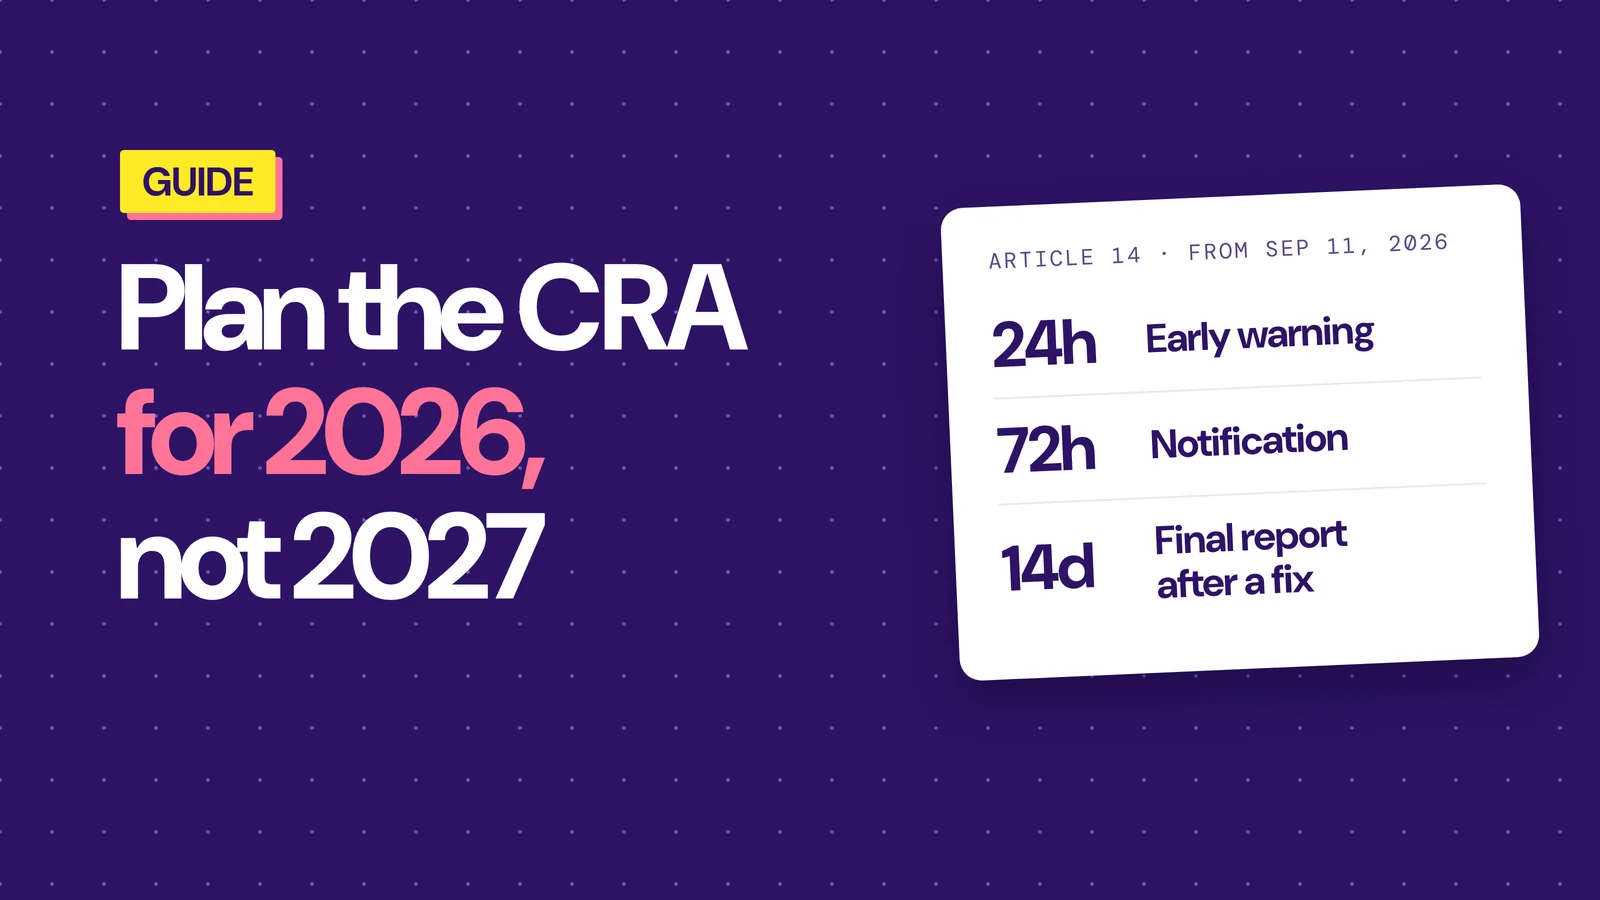
What the EU Cyber Resilience Act requires
A practical breakdown of what the EU Cyber Resilience Act requires by September 11, 2026 (Article 14 reporting) and December 11, 2027 (full applicability).
Read
Six months of silent secret scanning
A coding agent committed .env.bak to our main branch. Our gitleaks hook had been a silent no-op for six months. Here is what we rebuilt at the org level.
Read
Konvu is a Cyber Startup Award 2026 finalist
Konvu is a finalist for the Cyber Startup Award 2026 at Infosecurity Europe. Lucas will pitch on June 2nd and give a talk on vulnerability management on June 3rd.
Read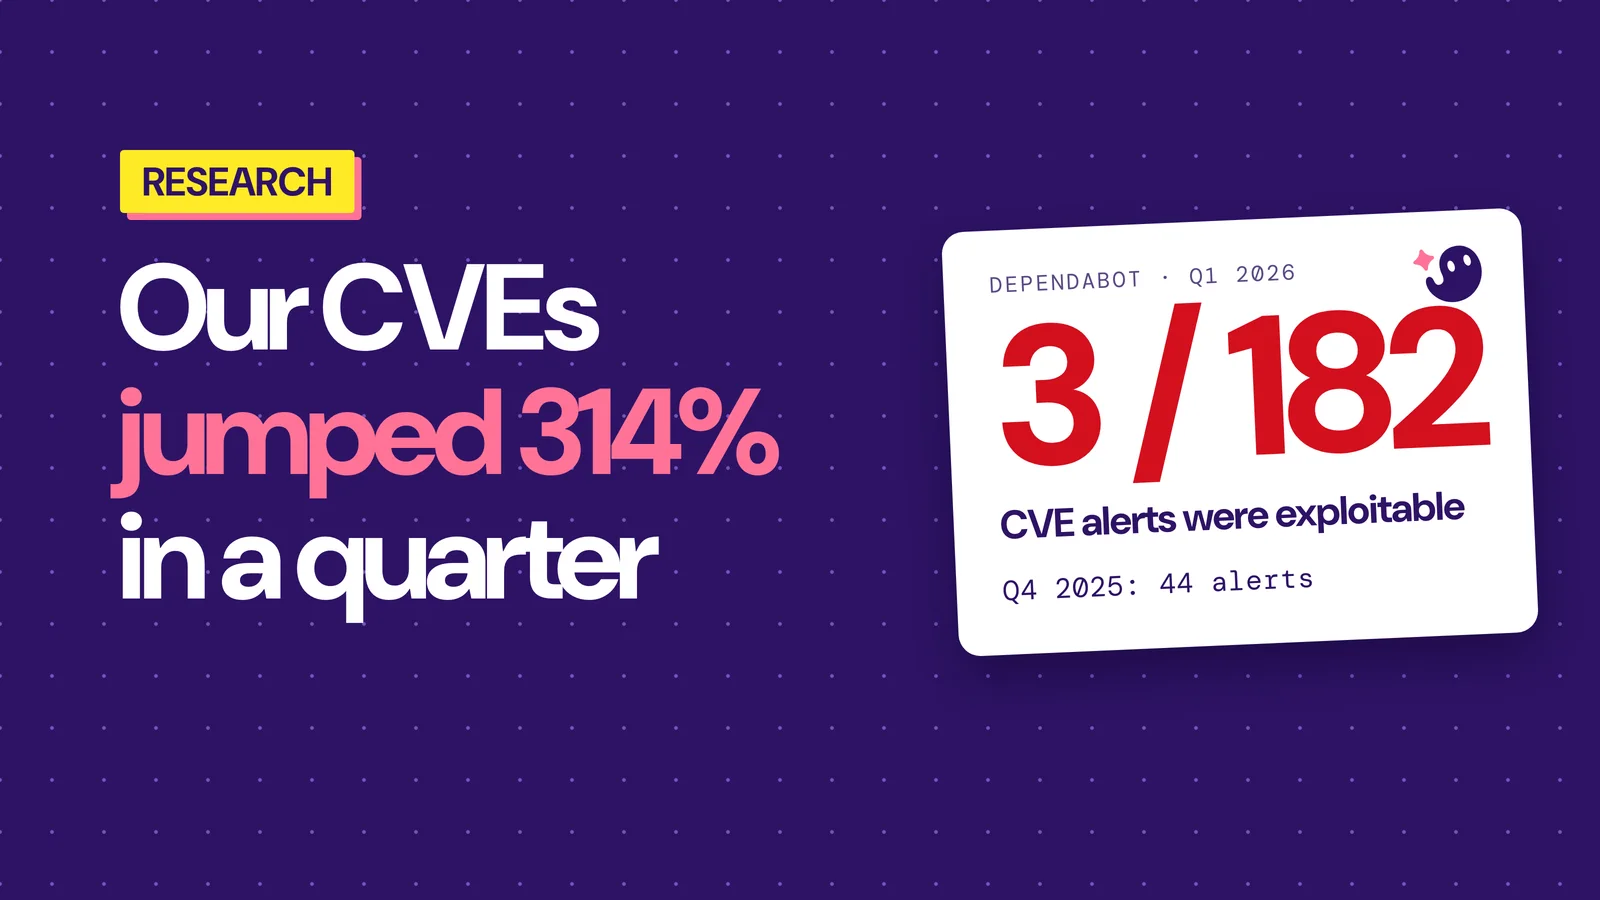
A quarter of CVEs on our own repos
Everyone quotes +30% CVEs in Q1 2026. On our own repos the number is +314% quarter over quarter. Under 2% were actually exploitable. Here is the data and what it means for AppSec teams.
Read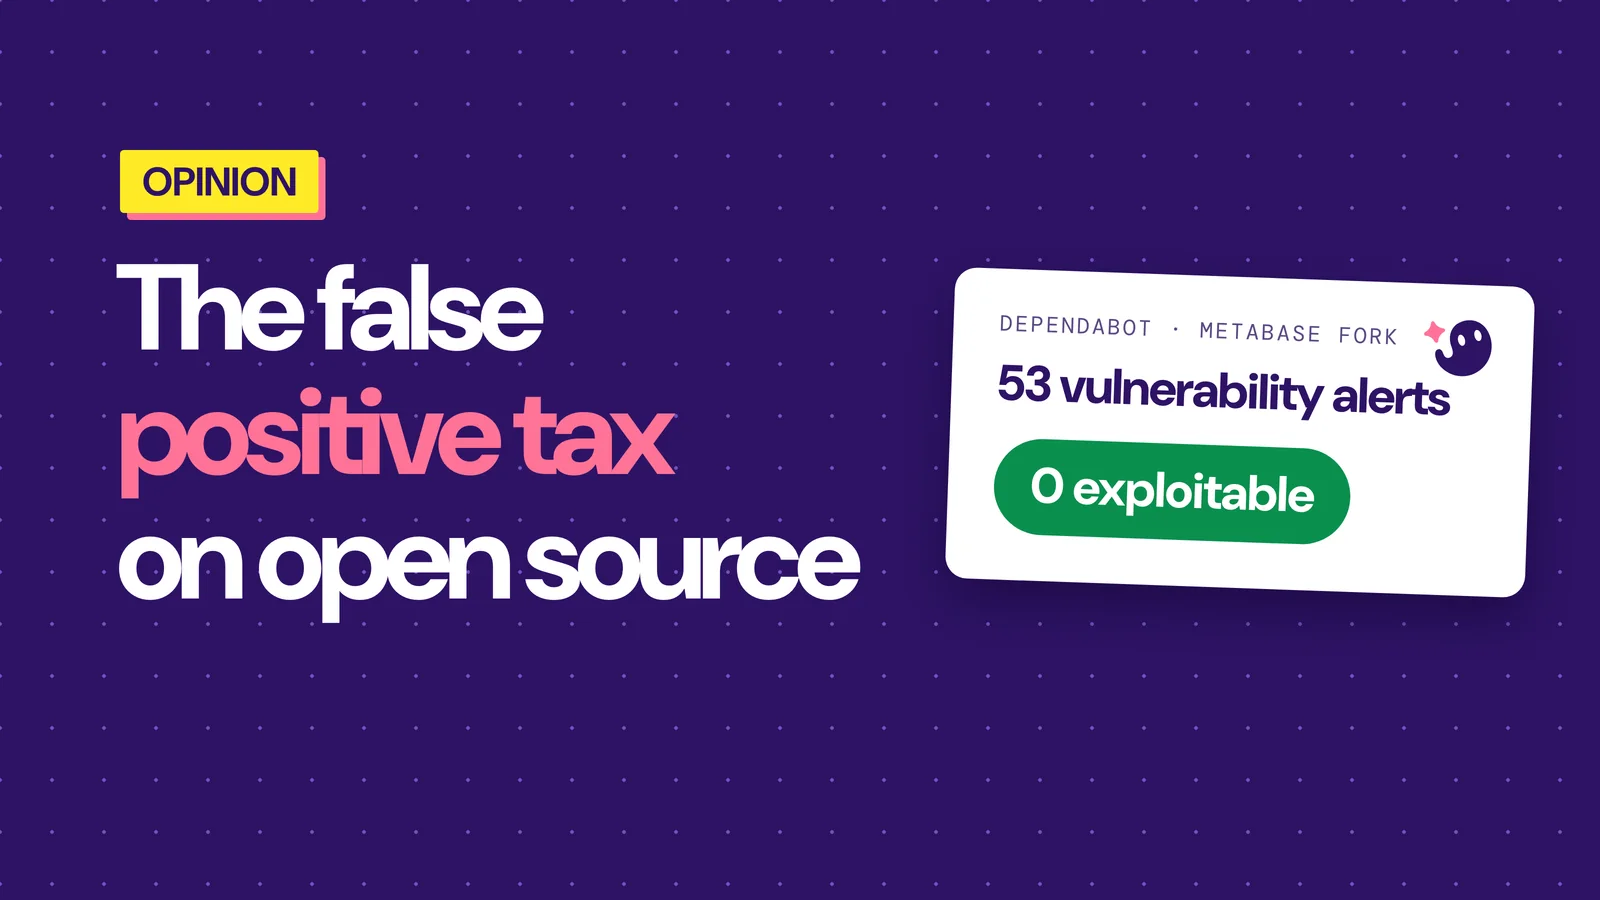
The False Positive Tax on Open Source
We forked Metabase, enabled Dependabot, and found 53 vulnerabilities. Every single one was a false positive. Open source vulnerability management is broken on both sides.
Read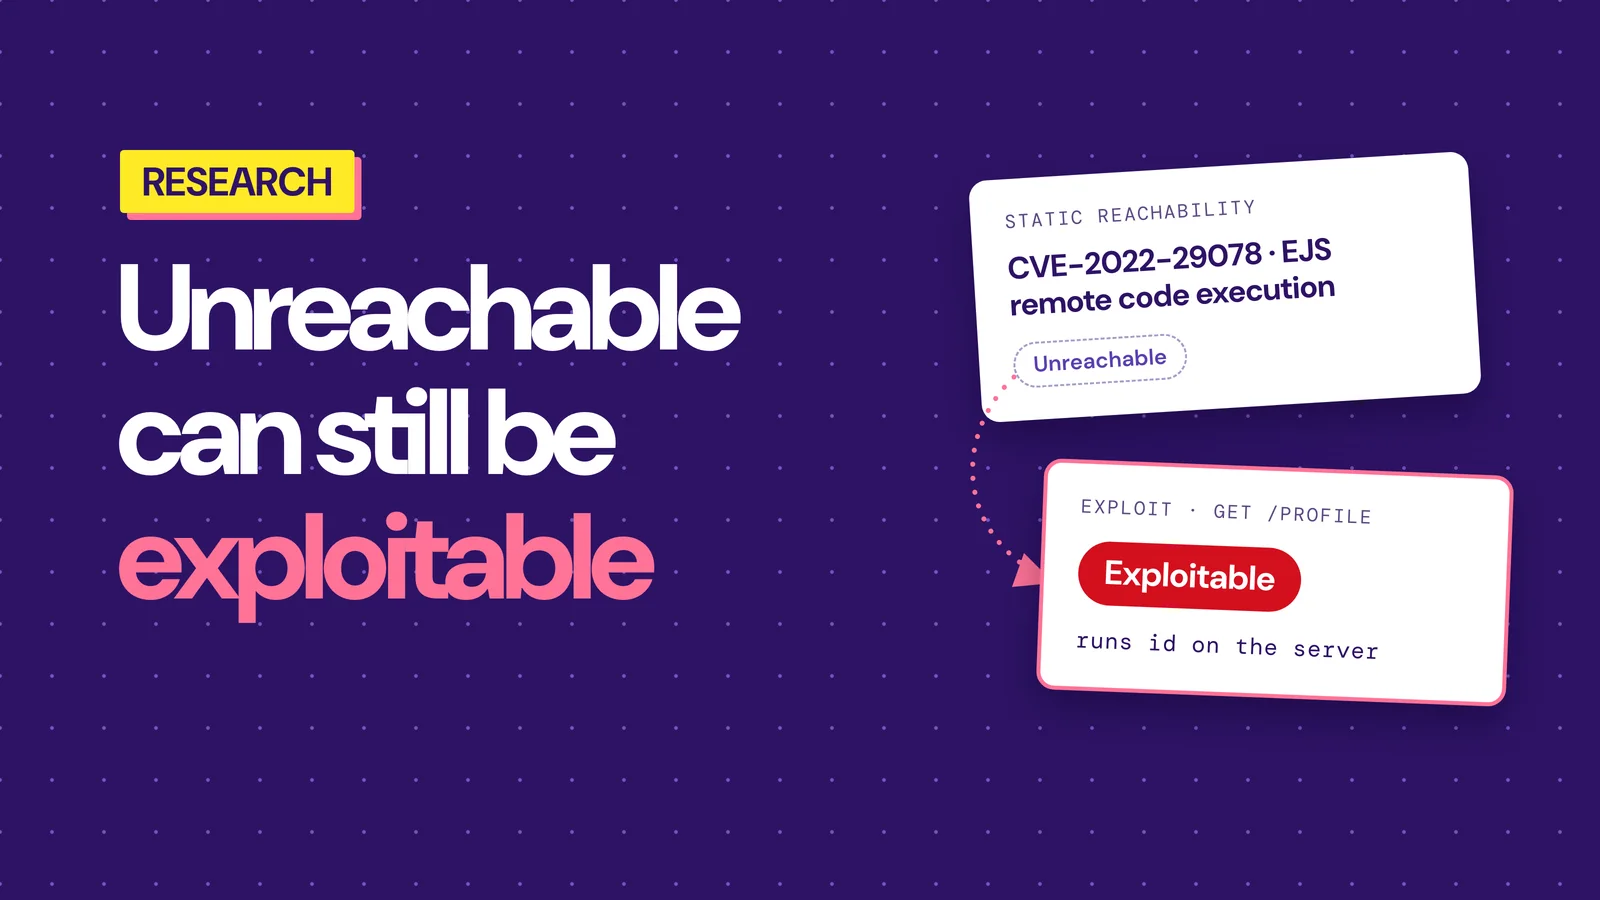
What Is Reachability Analysis (And Why It Misses Real Vulnerabilities)
Reachability analysis determines whether your app actually calls vulnerable dependency code. How it works, and four real CVEs where it gets the answer wrong.
Read
Automatically Reproducing Bug Bounty Reports with AI Agents
Reproducing a vulnerability from a bug bounty report means deploying someone else's app from scratch, at the right version, with the right config. We built AI agents that do it automatically.
Read
The Zero-Day clock is ticking. We showed the future of VM at RSAC LaunchPad.
Konvu pitched at RSAC LaunchPad 2026. Here's the problem we presented, what our customers helped us build, and what's next for vulnerability management.
Read
Konvu Selected as RSAC Launch Pad Finalist
Konvu has been selected as one of three finalists for the RSAC Launch Pad competition at RSAC 2026. We'll pitch our AI-powered exploitability engine to top-tier VCs on March 24 in San Francisco.
Read
Konvu Named a Supply Chain Innovator in the 2026 Latio AppSec Market Report
Konvu has been recognized as a Supply Chain Innovator in Latio's 2026 Application Security Market Report, validating our approach to exploitability analysis over simple reachability.
Read
How to Scale Vulnerability Triage Without Breaking Audit Requirements
Vulnerability volumes exceed human triage capacity, but auditors demand every finding accounted for. Evidence-based triage bridges the gap between scale and compliance.
Read
Why Static Code Reachability Is Not Enough: From "Reachable" to Truly Exploitable
Reachability vs exploitability: why a reachable function is not an exploitable one, and how exploitability analysis cuts false positives. Four real CVEs.
Read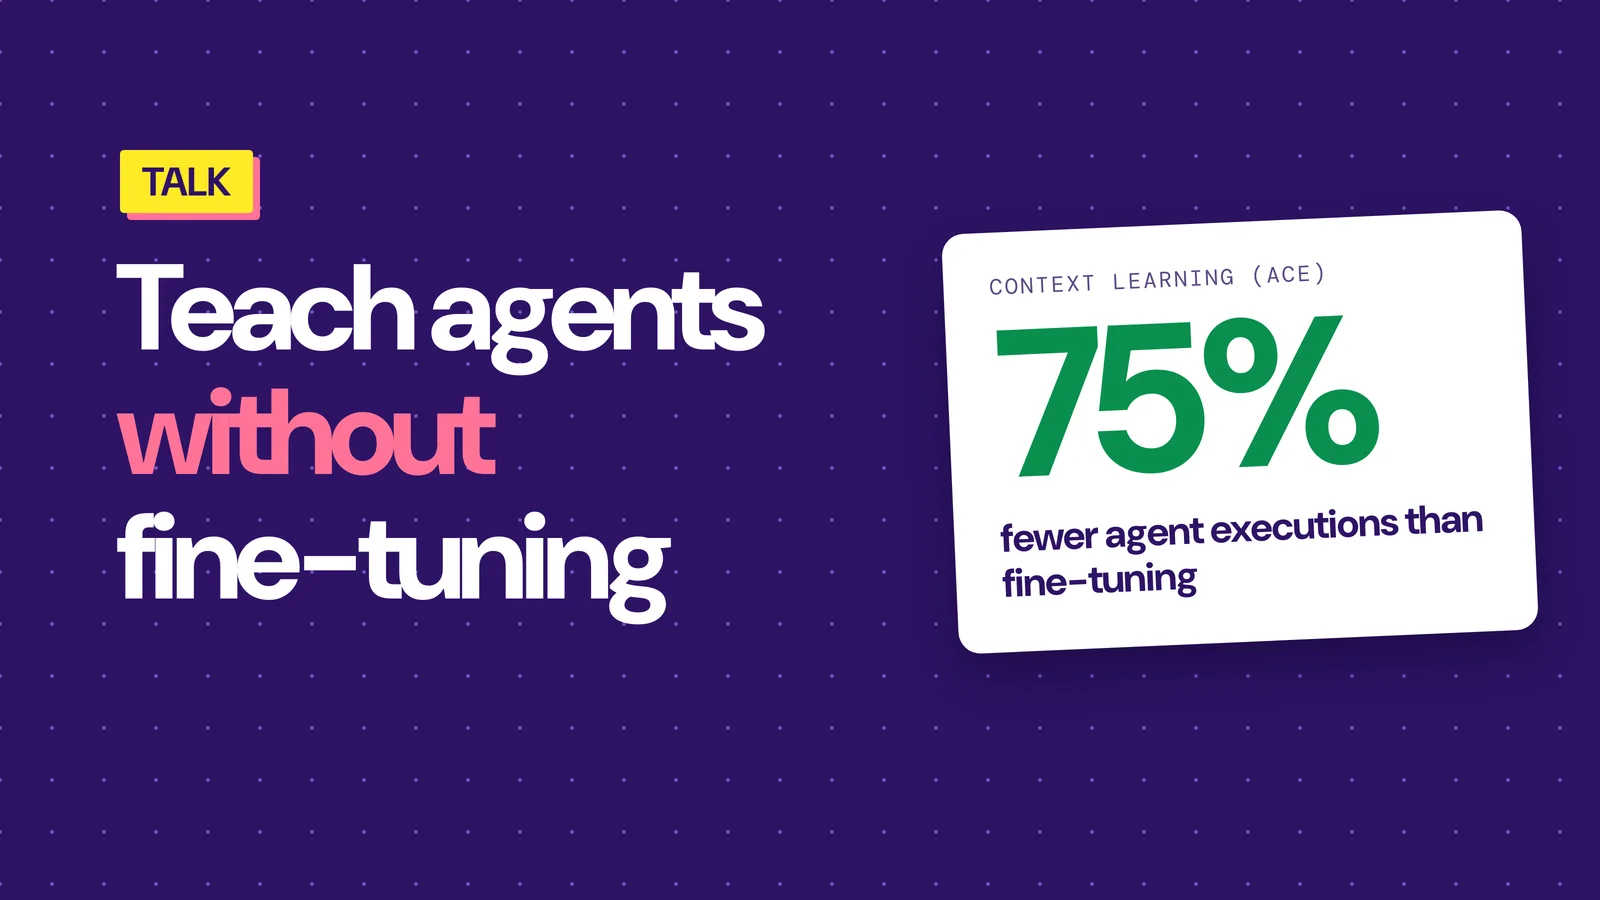
Teaching AI Agents Without Fine-Tuning with Context Learning
Konvupero Fall Edition welcomed Anyshift's Ghazi Felhi to explore Agentic Context Engineering (ACE) - teaching AI agents without fine-tuning.
Read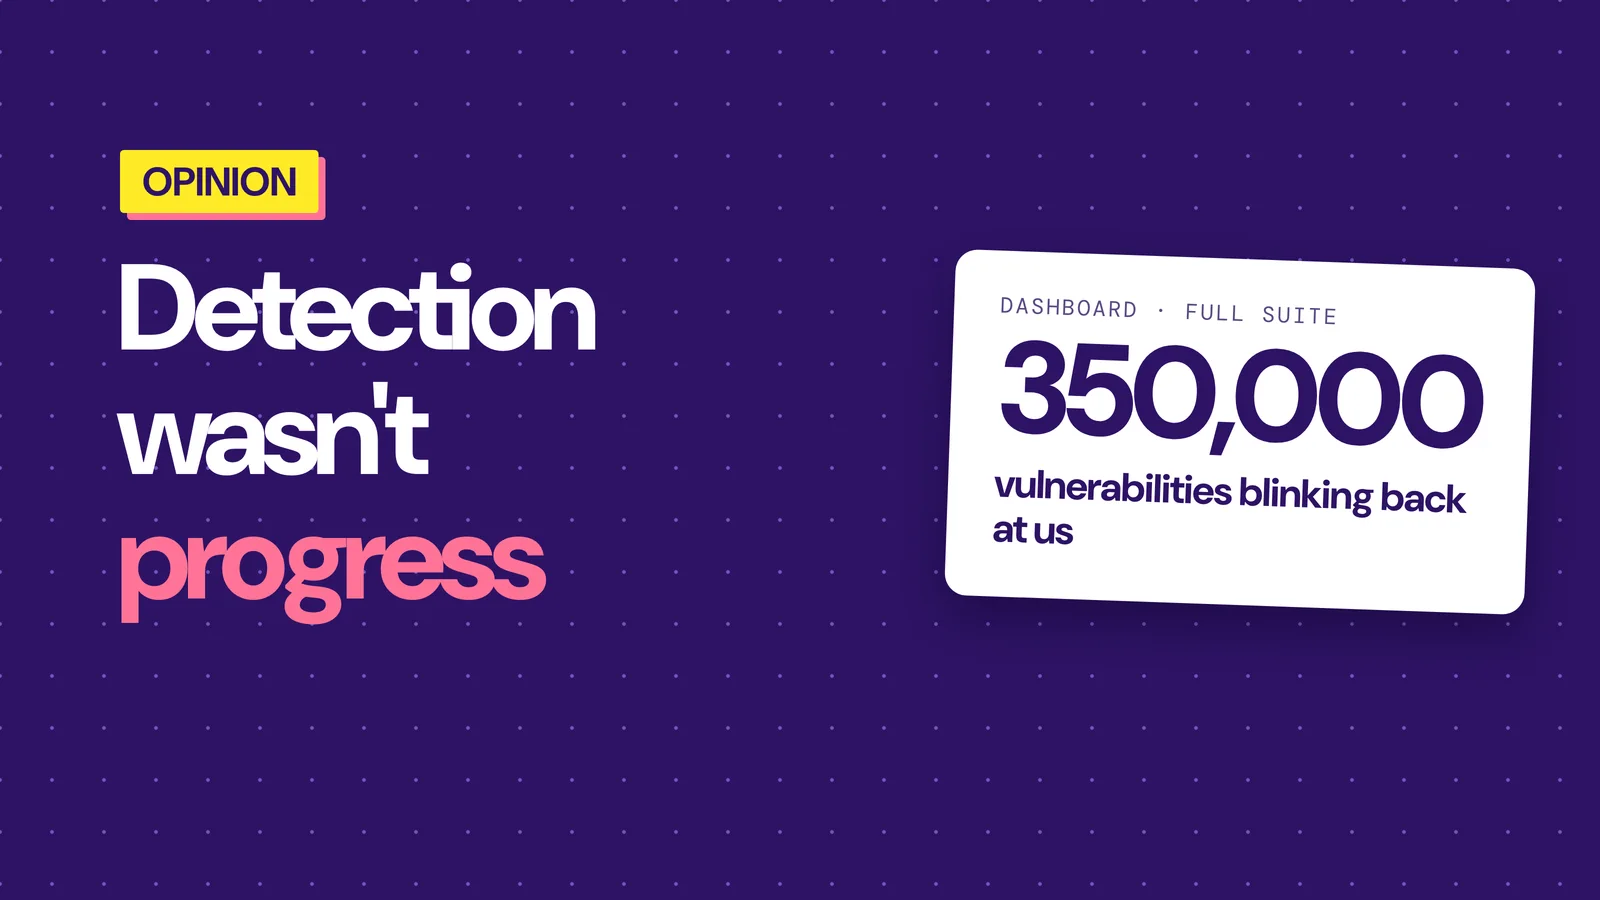
The Future of Vulnerability Management
For the past decade, security measured progress by vulnerability count. Detection wasn't progress, it was paralysis. Learn how agentic AI changes everything.
Read
Being a Junior Software Engineer in 2025
Being a junior engineer in 2025 looks different. AI handles repetitive coding, leaving higher-leverage problems that demand judgment, curiosity, and product intuition.
Read
Navigating Kubernetes: Hard-Won Lessons from Agent Injection Webhooks
A mutating webhook that intercepts every pod can deadlock your cluster at boot. How we scope namespaces, manage secrets, and run agent injection in production.
Read
You don't need an AI agent framework, or why frameworks are the new Juicero
A practical lightning talk on building AI agents without frameworks. Build the loop, add the tools, measure, then earn the complexity.
Read
Handling GitHub App Admin Approval Workflows
Enterprise GitHub App installs stall at admin approval. Capture the requester's context, match approvals back, and auto-activate with a fulfillment loop.
Read
How Konvu got its name
The real story behind the Konvu name and a repeatable, two-hour process you can use to pick a strong .com without drama.
Read
We helped build a YC Startup. Now we're building our own, The YC Way.
The YC principles we learned at Sqreen and still live by at Konvu. Build something people want, write code, talk to users, and focus on one problem at a time.
Read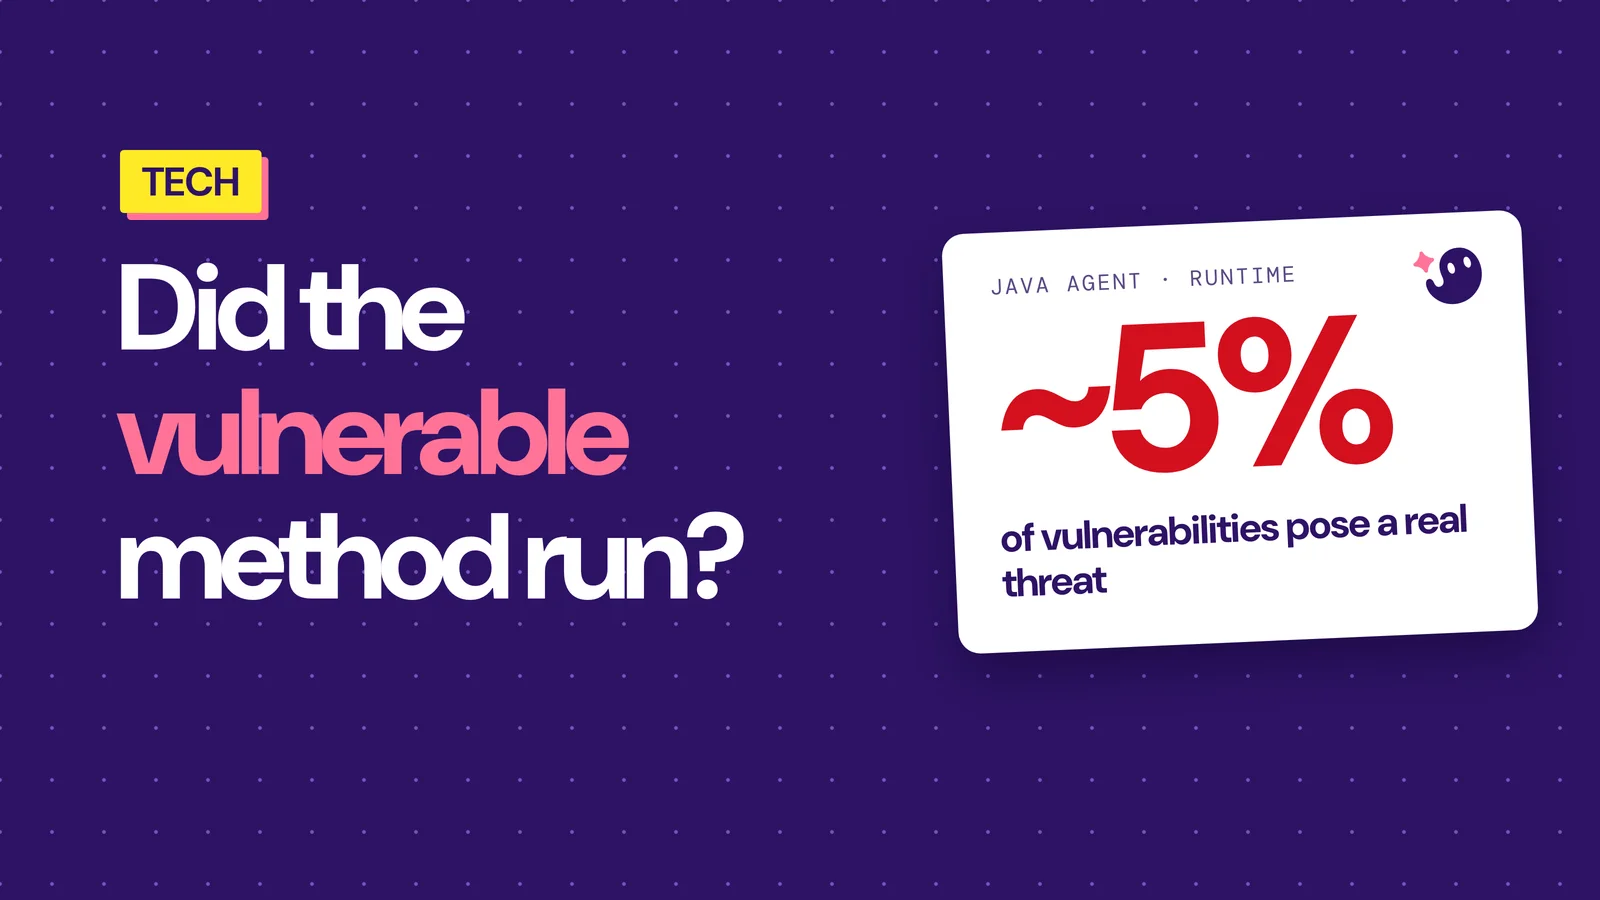
Using Java Dynamic Instrumentation to Detect Exploitable Vulnerabilities at Runtime
How Konvu uses Java dynamic instrumentation to identify truly exploitable vulnerabilities, reducing false positives and focusing remediation efforts.
Read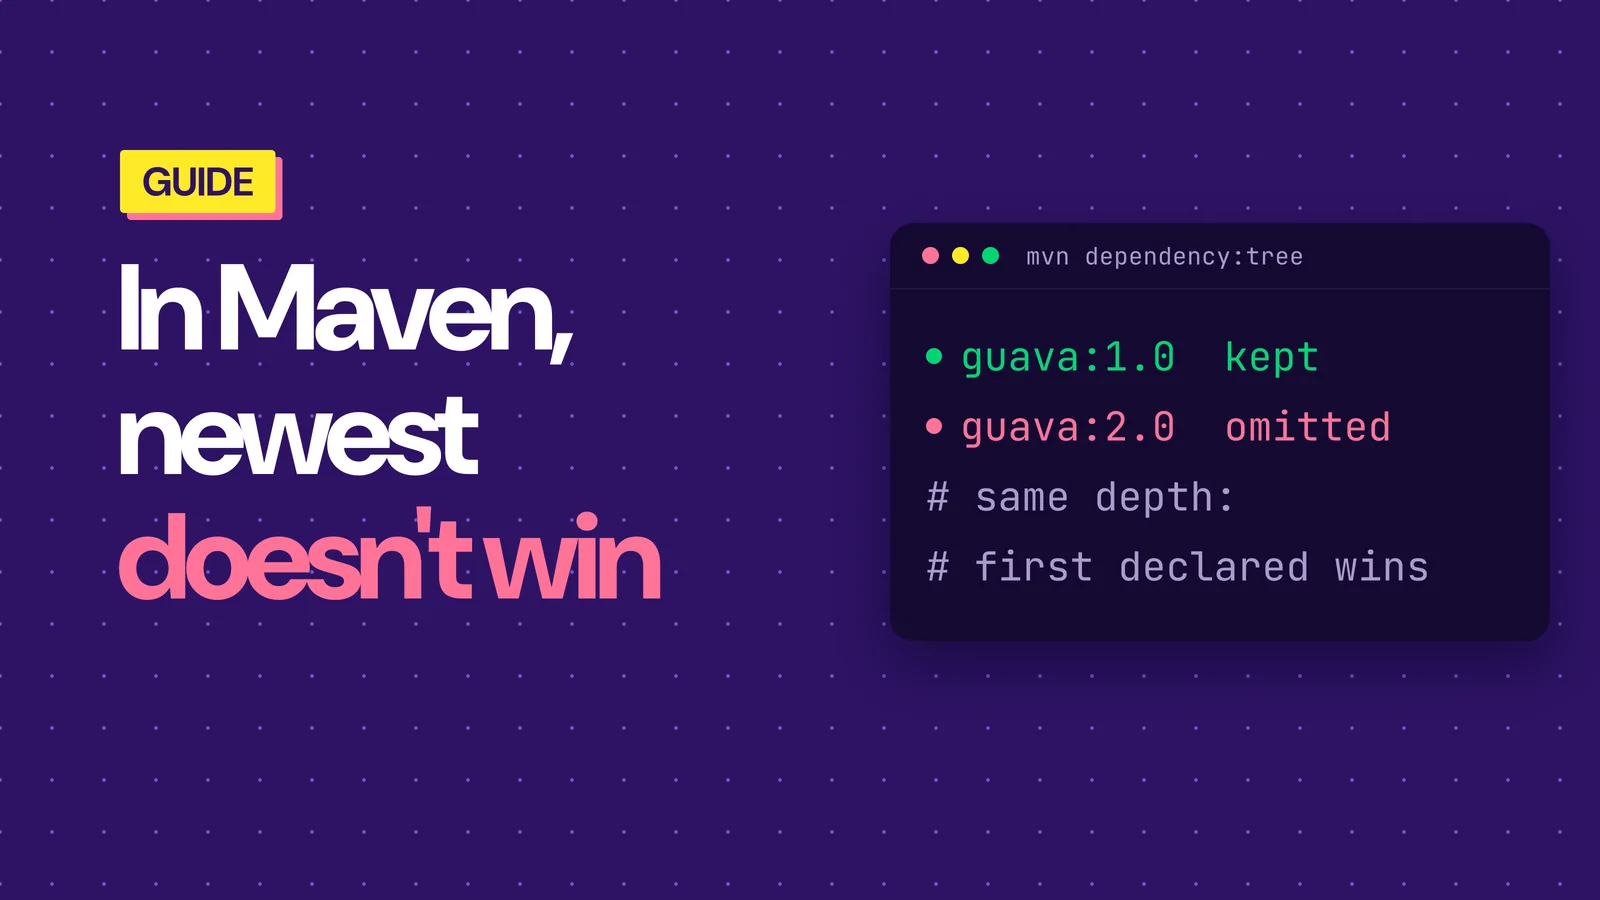
Navigating the Maze of Maven Dependencies - A Survival Guide
Maven picks the closest declaration, not the newest version. Trace conflicts with dependency:tree -Dverbose, fix them with exclusions and the Enforcer plugin.
Read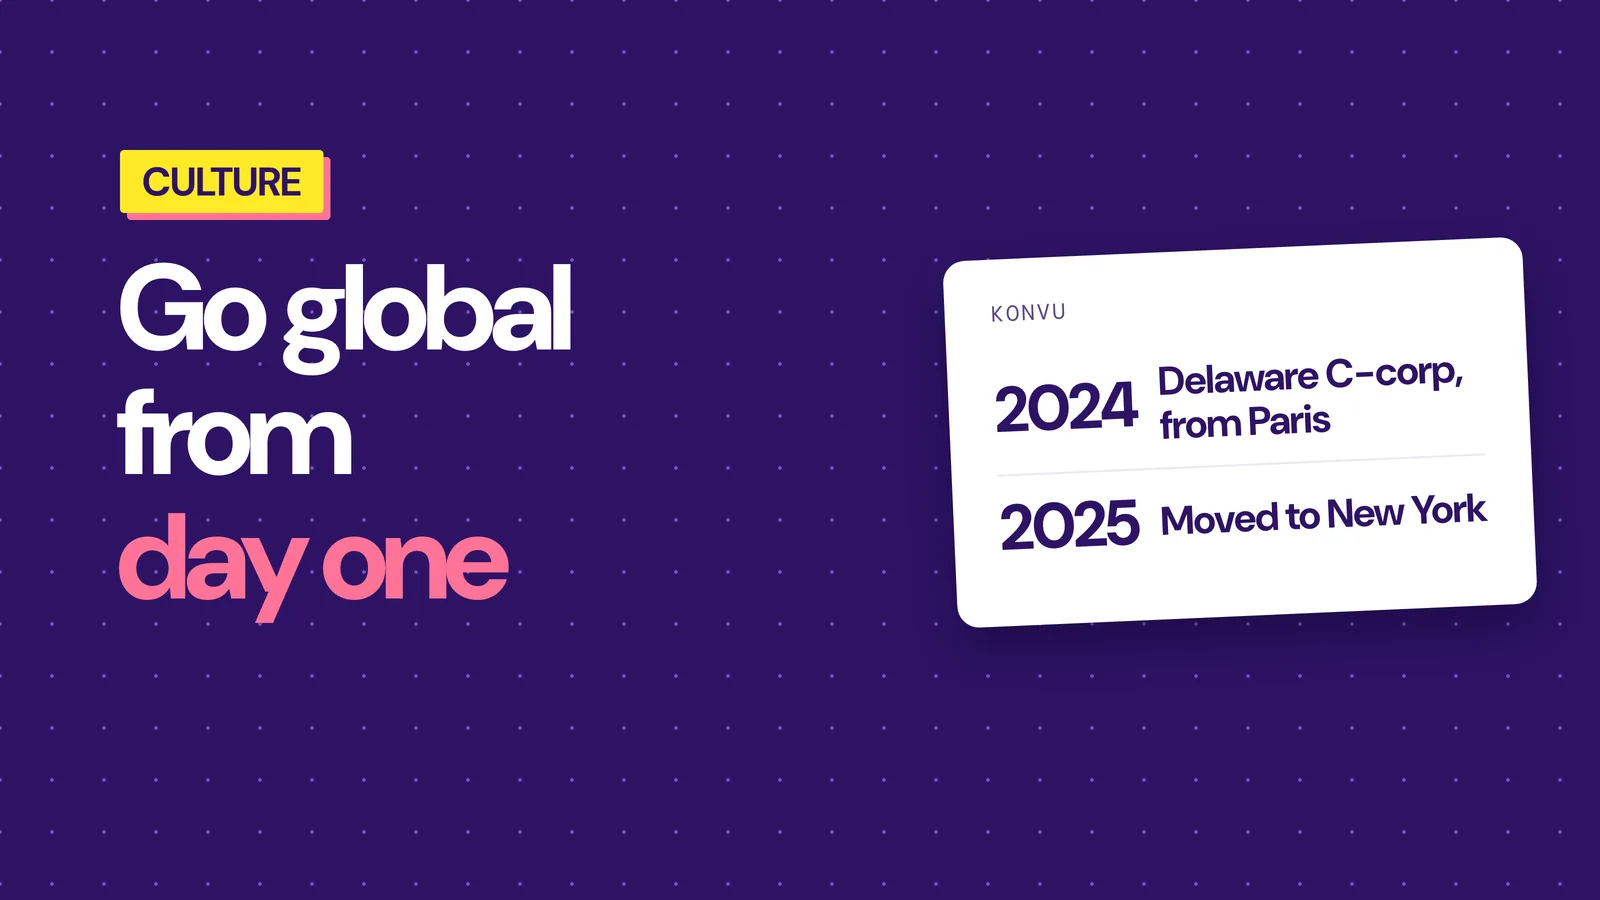
How We Built Konvu for Global Scale From Day One
How Konvu built a global company from day one - lessons from US incorporation, international culture, and early market commitment by European founders.
Read