See how Konvu helps
Every finding leaves with a decision attached: exploitable, false positive, or inconclusive. Not another number to sort by.
What changes
Six jobs your team stops doing by hand
The queue drains without a human opening each finding
Konvu reviews every finding your scanners produce and closes what isn't exploitable, cutting a typical backlog by about 95%.
Automate triage →Severity stops setting your order of work
A medium in an internet-facing service outranks a critical in a dormant internal tool. Konvu ranks by what is exploitable and what the asset is worth.
Prioritize by risk →A dismissal your team and your auditor both accept
Every dismissal names the code path Konvu checked and the condition that ruled the finding out, so a closed ticket holds up months later.
Reduce false positives →The fix ships, not just the verdict
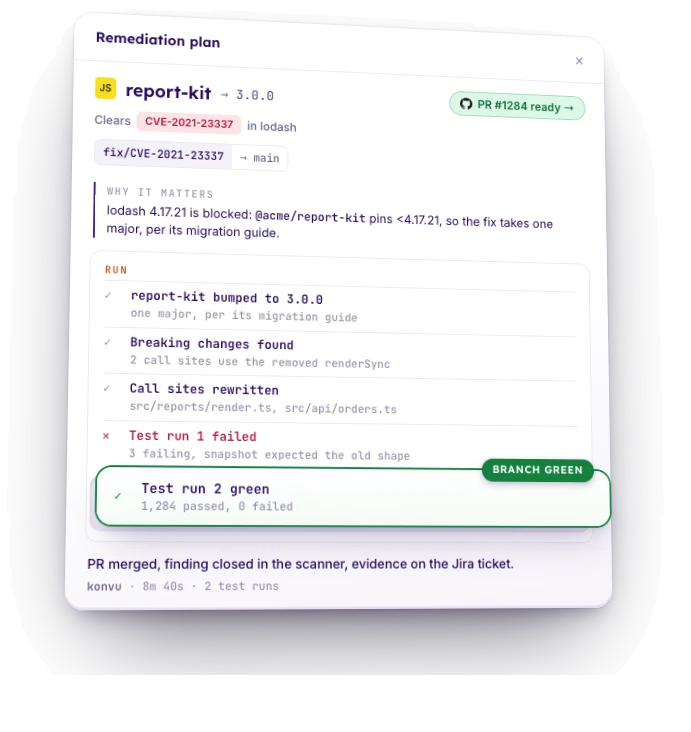
A reviewable pull request, for a dependency upgrade or for a finding in your own code, with breaking changes checked and your tests run before you see it.
Fix before exploits →The record survives the audit
Each verdict carries the reasoning trail behind it: the code Konvu read, the conditions it tested, what settled the call. The depth an auditor accepts rather than reopens.
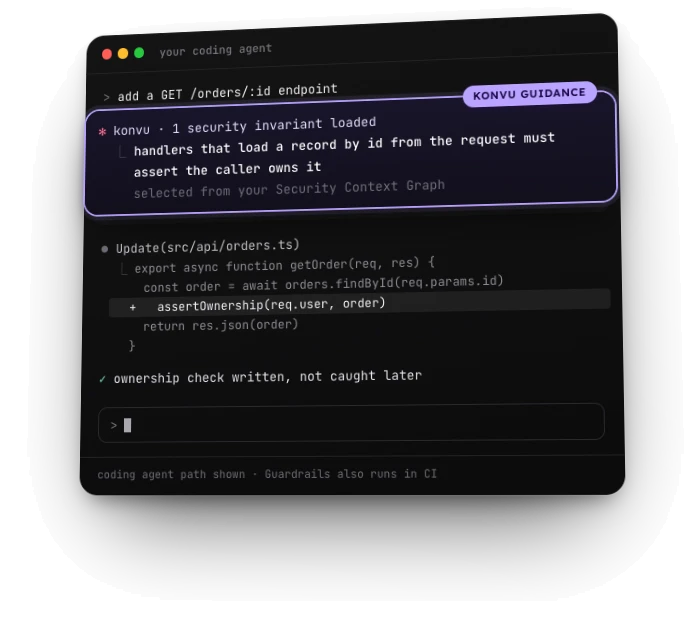
Meet compliance →The missing check gets written, not caught later
Konvu maps private application context into a Security Context Graph, derives the security invariants that matter, and checks relevant code changes in coding agents or CI.
Prevent vulnerabilities →How it works
One run, from flagged to fixed
Findings are investigated as they arrive rather than in a weekly batch, and every step leaves the evidence behind it in the tools you already run.
Connect the scanners and repos you already run
Konvu sits downstream of Snyk, Semgrep, Checkmarx, Trivy, Black Duck and others across SCA, SAST, container, cloud and secret scanning, plus the repos and ticketing behind them. Nothing to replace, nothing new for developers to learn.
Browse the full list of integrations →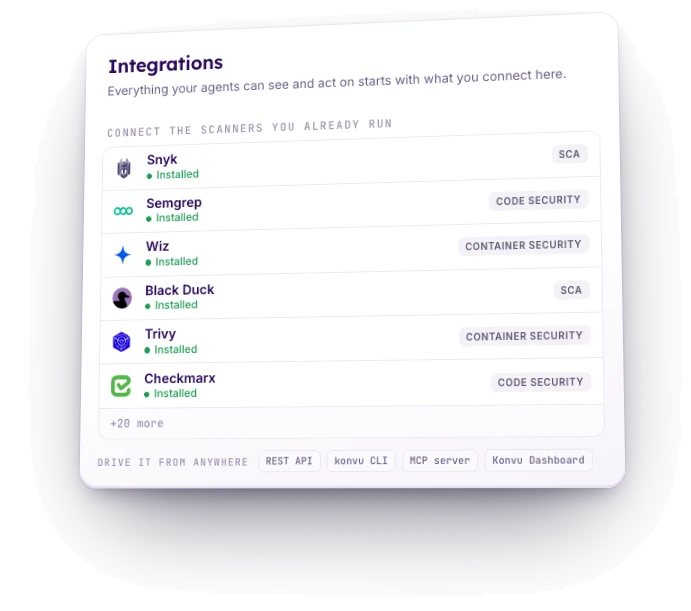
Build the context each finding needs
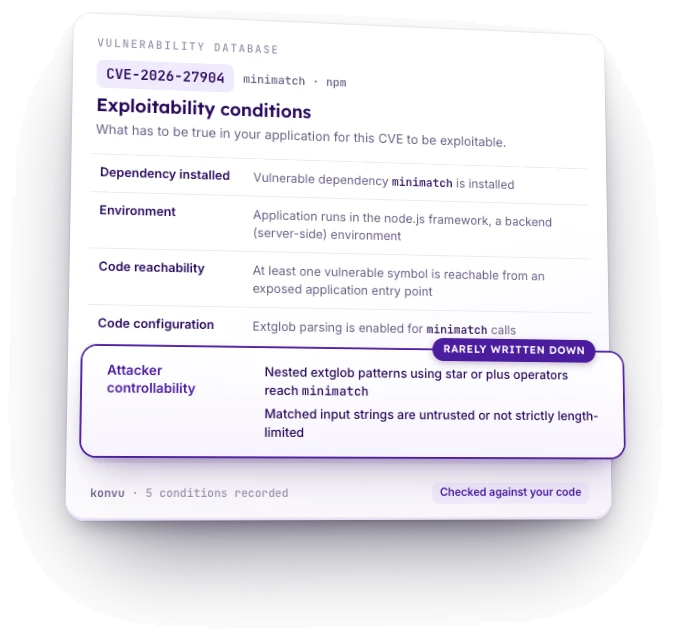
A CVE ID isn't enough to judge exploitability. Konvu pulls the dependency graph, the code path or the running image, then joins it to our vulnerability database, where the conditions that make each CVE exploitable are written down. For most vulnerabilities, nobody ever recorded them.
Prove what's exploitable
Konvu goes past reachable: whether attacker-controlled input actually reaches the symbol, whether a sanitizer sits in the way, whether the configuration the exploit needs is present. Reachable is necessary, not sufficient. About 95% of a typical backlog doesn't qualify, and every verdict ships with its evidence.
Go deeper on the reachability analysis →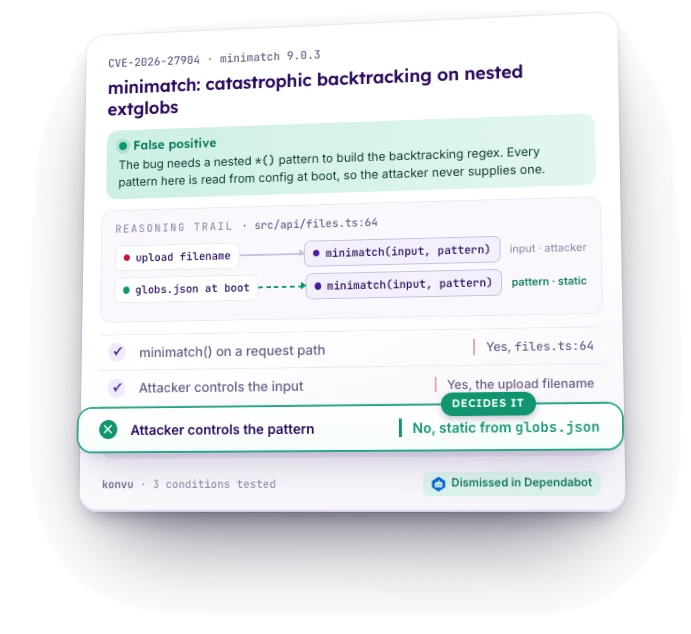
Ship the fix, not just the verdict
Konvu reads the upstream changelog, resolves the constraints blocking the upgrade, runs your test suite, and opens the pull request once it passes, with the CVE it closes and why the upgrade is safe attached. Findings in your own code go the same way.
Help stop the next one from shipping
The first four steps clear what already exists. Guardrails works earlier on business logic risks such as tenant isolation, entitlements, approvals, state transitions, and money movement. Konvu maps private application context into a Security Context Graph, derives security invariants, and checks relevant changes in coding agents or CI before review and merge.
Recognition
"The platform delivers two key outcomes: vulnerability prioritization and remediation, and is well positioned to solve both effectively."
James Berthoty, Founder at Latio
Read the full report →Where Konvu fits
Detection is solved. The decision is not.
Your scanners are good at one question. Is this weakness present in what we ship?
Konvu answers the one that decides whether anyone works on it. Can an attacker use it, here, in this deployment?
What the scan gives you
- A finding, a severity band, a path
- A score calculated once, for everyone who has the finding
- Reachability, at best
- No reasoning attached
What Konvu adds
- The condition that decided it, checked in your code
- Whether anything attacker-controlled can reach it
- Whether the configuration the exploit needs is present
- A dismissal your team can defend, evidence attached
Same finding. One of them you can act on.
What you control
You decide how much runs without you
Recommend only
Konvu investigates and posts its verdict with the evidence. Nothing moves until a person acts on it.
Act with approval
Konvu prepares the change and waits for a person. That can be a pull request your team reviews, or a remediation plan handed to whichever coding agent you already use.
Autonomous
Konvu closes what it has proved and ships what it has tested, and every action stays in the audit trail.
You decide, and you can change your mind. Konvu takes no action you have not allowed, nothing it does is one-way, and a verdict you disagree with reopens with your reasoning next to Konvu's.
Your code
Two deployment models
Run Konvu Cloud, or our Kubernetes controller inside your own cluster, where Konvu never has access to your source. SOC 2 Type II certified, and your code is never used for training. Connecting a scanner and a repository takes hours, with nothing to install on developer machines.
How Konvu handles your code and data →Pricing is based on triage verdicts delivered, not seats. See the plans.