Konvu Guardrails Datasheet
More people ship code than ever, and most of them have never read your security guidelines. How Konvu Guardrails drafts checks from your code and context, and how the coding agent and CI follow them, whoever prompts the change.
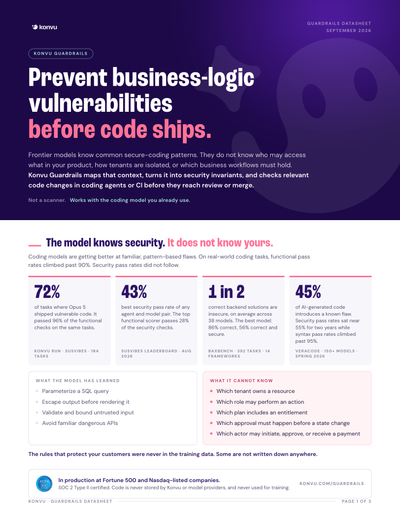
3 pages · PDF
Inside
- 01
The guidelines exist. Nobody writing the code reads them. Where they live today, and why review cannot close the gap.
- 02
What a generic check knows, and what only your guidelines say. Tenant scope, admin-only roles, approval steps, signing helpers, session middleware.
- 03
Five steps: read the code and context, draft the rules, edit and add your own, followed in the coding agent, checked in CI with a recorded decision.
- 04
The same change with and without the rule, prompted by a PM in Claude Code, on a real cross-tenant route.
- 05
Hooks and CI, independent: inside Claude Code, Codex, Cursor and other coding agents, or in CI with no agent at all.
- 06
Where CODEOWNERS, rules files, SAST custom rules, and AI reviewers stop. Evidence and control for AppSec. Who it is built for.
In production at Fortune 500 and Nasdaq-listed companies. SOC 2 Type II certified.
Get the PDF
Fill this out and the download unlocks on the next page.
Prefer a walkthrough? Book a demo